
Local service guide
Data Recovery and Backup in Lincoln, NE
Arrange Data Recovery and Backup in Lincoln, NE by requesting a device assessment, a check of usable backups and a written recovery quote before authorizing work. For ongoing service, require a restore demonstration and data-handling terms. If you suspect ransomware, isolate affected systems and involve an incident-response specialist. CISA recommends isolation first and restoration on a clean network. [4]
Match the provider to the recovery problem
Describe what happened, which device holds the files and what you have tried. List the operating system, storage type, encryption status and last known usable backup. Confirm whether the provider performs recovery at its own premises or transfers your device elsewhere. Request the receiving company's name and data-handling terms before approving a transfer.
For suspected ransomware, choose a provider with incident-response capability alongside recovery. CISA explains that attackers can encrypt files and steal data. Its response checklist starts with identifying affected systems and isolating them. Disconnect affected devices from Ethernet or Wi-Fi where feasible, coordinate with your response lead and use phone calls for incident communications. [4]
Let the responder guide shutdown and evidence preservation. CISA recommends powering down an infected device only when network isolation is impossible because shutdown loses potential evidence held in volatile memory. [4]
Get a quote with approval limits
Compare written quotes for the same recovery scope. Request separate charges for assessment, attempted recovery, delivery media and shipping. Have the provider explain what you owe if it retrieves no useful files or only part of your requested data. Set a spending limit and require your approval before additional work.
Prioritize the accounting database, current customer jobs, payroll files or other records you need to reopen. Request an assessment date, a separate recovery estimate and the conditions that could change either. Before accepting delivery, obtain a file inventory and check that priority files open on a suitable clean device. Specify who will verify that any recovered business application works.
Specify backup service through a restore test
Have the provider demonstrate recovery of a representative file and business application. Decide how much recent work you can afford to lose and how long you can operate without the system. Use those limits to define backup frequency, restoration priorities and support arrangements. Name the person who checks failed-backup alerts and the person who authorizes a restore.
CISA recommends offline, encrypted backups of critical data and testing their availability and integrity in a disaster-recovery scenario. It warns that ransomware can delete or encrypt accessible backups. Require the provider to identify the isolated copy, explain access to encryption keys during an outage and document restore-test results. [4]
For cloud backup, review permissions, deletion protection, retained versions and your exit process. CISA recommends limiting third-party access to assigned responsibilities and formalizing security requirements in contracts. It cautions that immutable storage requires attention to configuration, cost and regulatory suitability. Have the provider explain its proposed settings and how you retrieve your data when service ends. [4]
Prepare for an outage at your premises
Commission a recovery test that assumes you cannot use the office computer, local backup appliance or normal internet connection. Keep a printed contact list and agree on an alternate device or location for essential work. For an uninterruptible power supply, request a shutdown test under the actual equipment load and a plan for outages that exceed its runtime.
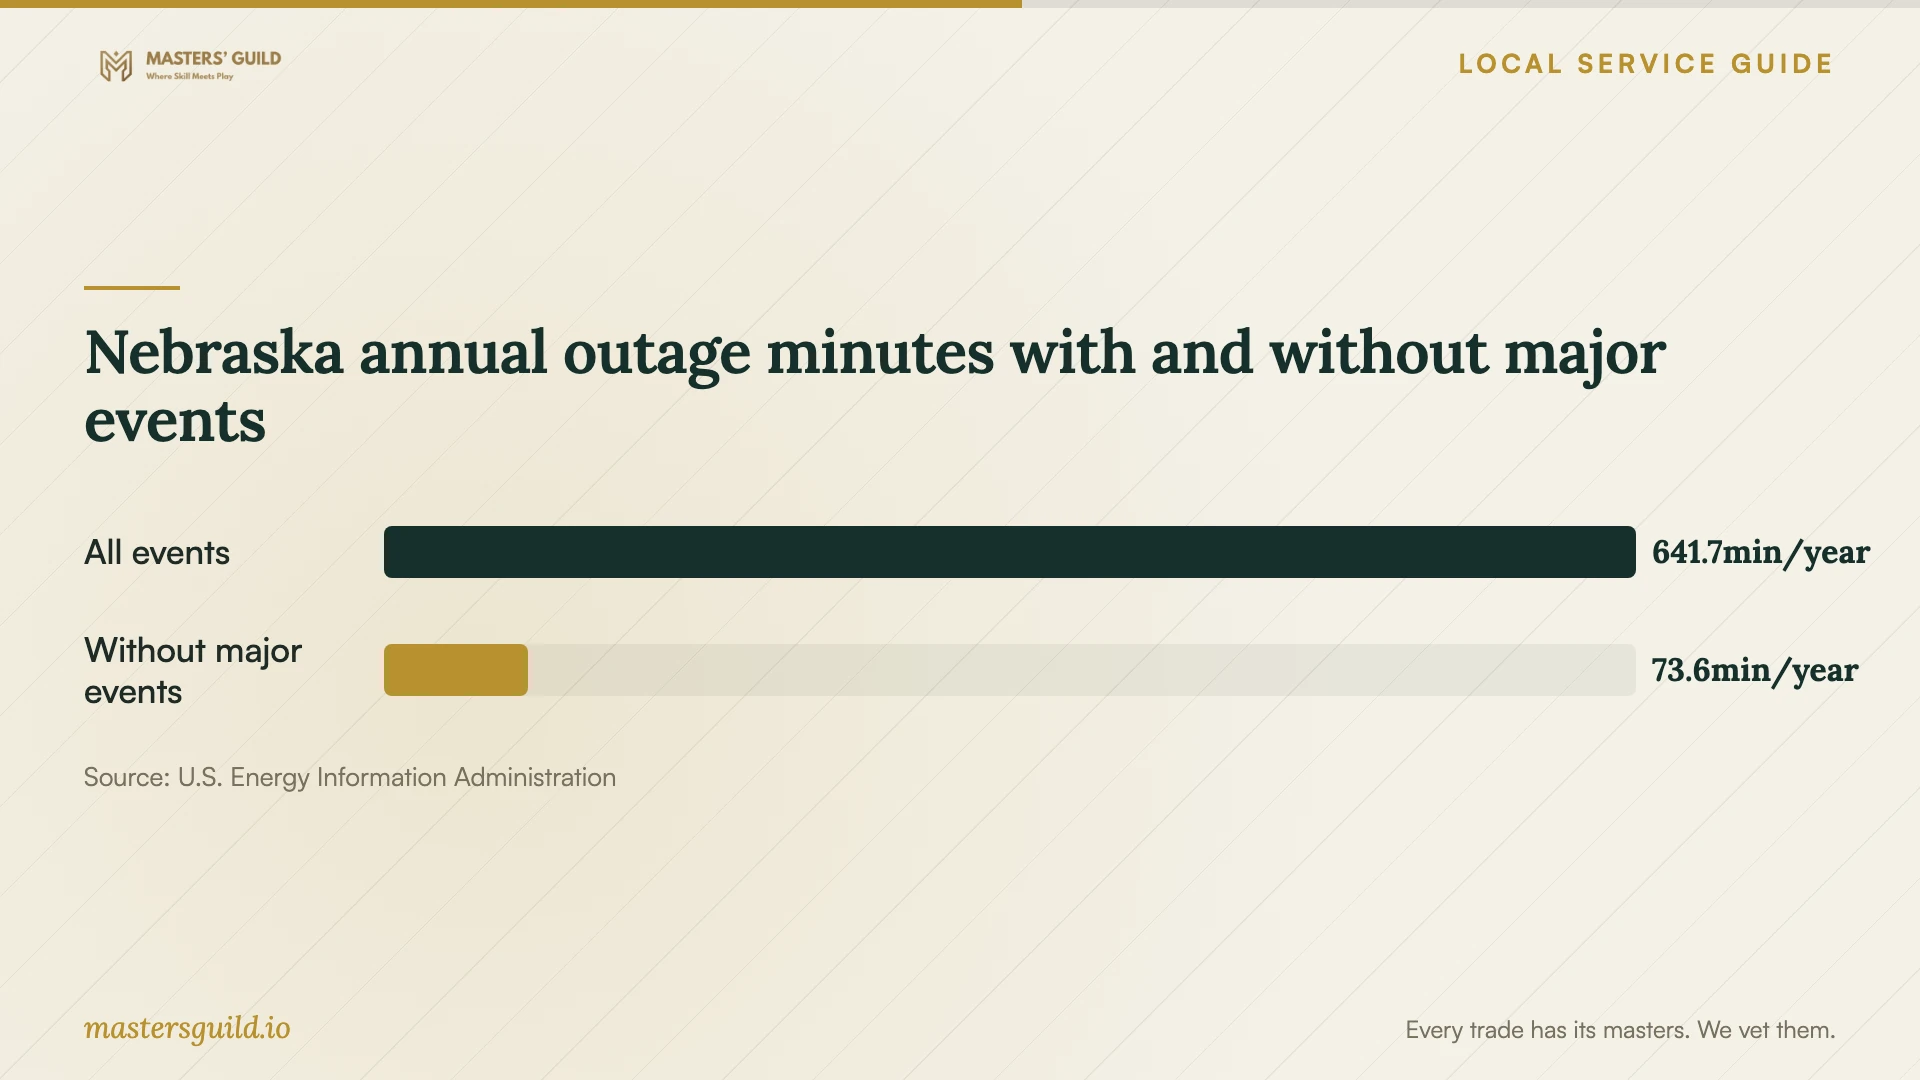
Use the Nebraska chart as regional context. EIA reports 641.7 minutes of average annual non-momentary interruptions including major events in 2024, compared with 73.6 minutes excluding major events. These statewide figures do not describe a particular Lincoln address or one outage's duration. Base your continuity requirements on the equipment and business functions you need. [5]
Agree on privacy and incident responsibilities
Before transferring customer or employee records, establish who may access them, where working copies reside, which subcontractors receive them and when the provider disposes of them. Section 87-808 requires reasonable safeguards for Nebraska residents' personal information, including disposal safeguards, and addresses contractual security requirements for disclosures to nonaffiliated service providers. [2]
Subsection (3) also permits compliance with those security and contract provisions through a state or federal law providing greater protection, or through GLBA or HIPAA regulations for entities subject to them, as specified in the statute. The contract provision excludes agreements entered before July 19, 2018, but applies upon renewal on or after that date. Have counsel determine which route and requirements apply to your business and agreement. [2]
For suspected unauthorized access, arrange investigation alongside recovery. Under section 87-803, businesses conducting business in Nebraska that own or license computerized Nebraska-resident personal information must conduct a reasonable, prompt, good-faith investigation after learning of a security breach. Resident notice depends on whether unauthorized use occurred or is reasonably likely. When resident notice is required, the business must notify the Attorney General no later than it notifies residents. Have counsel assess notice obligations and any lawful delay. [3]
Nebraska annual outage minutes with and without major events
Local details that affect your job
LES storm experience calls for off-premises access
LES reported 18.4 minutes of average annual interruption per customer in 2025, excluding storms. Its report also describes a blizzard leaving 12,600 customers without service and a wind event causing outages for more than 38,000 customers. Require a demonstration of backup access from outside your premises. Size power protection through equipment testing; the annual average does not establish a suitable battery runtime. [1]
Review Nebraska security terms before transferring records
Section 87-808 addresses contractual safeguards when a business discloses Nebraska-resident personal information to a nonaffiliated provider. Subsection (3) allows alternative compliance through more protective state or federal law or qualifying GLBA or HIPAA regulations for entities subject to them. The contract provision excludes agreements entered before July 19, 2018, until renewal on or after that date. Before transferring records or renewing an older agreement, have counsel determine the applicable requirements and put the provider's responsibilities in writing. [2]
Choose the work to request
| Situation | Service to request | Approval question |
|---|---|---|
| Files missing from one device | Device assessment and scoped recovery | Which priority files will you attempt, and what do I owe for a partial result? |
| A backup is available | Restore assistance and verification | Can you demonstrate that the required files and application work? |
| Ransomware is suspected | Incident response, isolation and clean-network recovery | Who preserves evidence and assesses the recovery environment? |
| Ongoing backup needed | Offline encrypted backup and restore testing | Which copy remains isolated, and who checks test results? |
| Customer personal information involved | Data-handling agreement reviewed for applicable Nebraska requirements and alternative compliance | Has counsel determined which security and contract provisions apply? |
Your hiring checklist
- Record the device, symptoms, incident timeline and previous recovery attempts.
- List priority files, applications and the last backup you have checked.
- Confirm who performs recovery and whether another company receives devices or data.
- Get assessment charges, unsuccessful-recovery terms and an approval limit in writing.
- Agree on access, encryption, working-copy retention and disposal; have counsel review applicable security terms.
- Request a representative restore test and document the result.
- Keep recovery contacts and essential access instructions available outside the affected premises.
Frequently Asked Questions
Can I approve assessment before knowing the recovery price?
Approve a defined assessment with a spending limit. Require a revised proposal before additional work. Clarify charges for unsuccessful attempts, partial recovery, shipping and return media, and identify the files that count as a useful result.
How do I judge a managed-backup proposal?
Request a restore demonstration, written retention terms and a named person responsible for failed-backup alerts. CISA recommends offline, encrypted critical-data backups and tests of their availability and integrity. Have the provider explain how its service implements those practices. [4]
Should I restore a backup as soon as ransomware appears?
Contact an incident-response lead and isolate affected systems first. CISA recommends prioritizing restoration on a clean network and avoiding reinfection. Have the responder guide evidence preservation and assess the compromise before reconnecting restored systems. [4]
Does a failed drive require breach notification?
A drive-failure report alone does not establish the findings that trigger notice under section 87-803. The statute addresses security breaches and investigation of unauthorized use. Have counsel assess suspected unauthorized access, investigation findings and any required resident and Attorney General notices. [3]
Sources and scope
This guide combines the sources below with practical planning guidance. Figures apply to the stated geography and period; request a written quote for your property.